Cyber resilience requires the board and the CISO to be aligned
A recent Deloitte study disclosed that a meager 38% of Chief Executive Officers and 23% of board members were “highly engaged” in the
cli:~$ Blog · Insights for cyber leaders
Writing for the people who carry cyber risk into the boardroom — strategy, governance, career moves and the practical craft of leading a security function.
Page 4 of 6 — 66 articles across 30 topics.
A recent Deloitte study disclosed that a meager 38% of Chief Executive Officers and 23% of board members were “highly engaged” in the

The COVID-19 pandemic has shattered several businesses, and those companies left afloat were plunged into uncharted waters. Several cybersecurity teams (already under tremendous pressure

Most cybersecurity professionals have ambitions to rise to the chief information security officer (CISO) role. Very few, however, ever realize
A Google search for “how to break into cyber security” returns more than 88 million results. There are numerous blogs,
The significance of passwords is hard to overstate. They protect online banking accounts from internet thieves, intellectual property from unscrupulous
A recent Harvard Business Review article stressed, “Spending millions on security technology can certainly make an executive feel safe. But the major
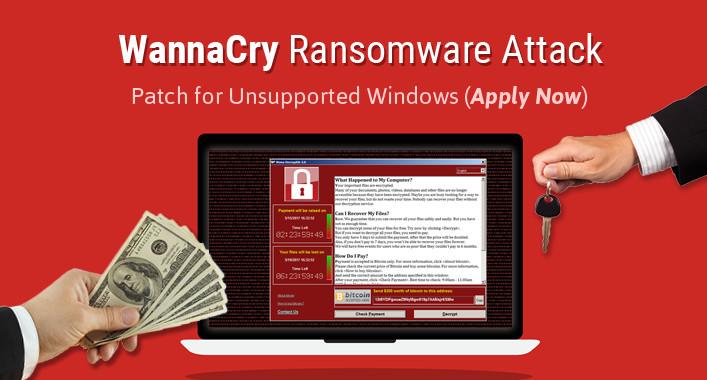
The attack on the UK’s National Health Services (NHS) – which forced up to 40 hospital trusts to cancel surgeries

Back in 1898, the New York Times published a fascinating article, An Old Swindle Revived, in which it lamented the rising number of
Embracing new technologies affords pharmaceutical companies opportunities to innovate, lower operational costs and derive vital business insights. More importantly, these

Executive support matters now more than ever History has taught us that senior business officers are ultimately held accountable for
Back in September 2016, St. Jude Medical Inc. sued security research firm MedSec and investment research outfit Muddy Waters, accusing them of
For several years, even during times of conflict, medical institutions have been considered sacred places – thus immune from deliberate attacks.
Join the Cyber Leadership Hub for free and receive our monthly newsletter with practical leadership insights, CISO success stories and career-building ideas.